BastionBBastion // Local Defensive Sensor

 ____    _    ____ _____ ___ ___  _   _
| __ )  / \  / ___|_   _|_ _/ _ \| \ | |
|  _ \ / _ \ \___ \ | |  | | | | |  \| |
| |_) / ___ \ ___) || |  | | |_| | |\  |
|____/_/   \_\____/ |_| |___\___/|_| \_|
            

Bastion : Defender Watchdog
& Local Defensive Sensor

Microsoft Defender protects your machine. Bastion watches the gaps. Bastion is not an antivirus. It is an open-source local sensor that runs alongsideDefender and covers the surfaces Defender doesn't show you — its own tamper state, persistence drift, camera and mic access, USB, canaries — with a tamper-evident event history and human-readable receipts for every action.

The names aren't an accident. A bastion is the projecting wall that gives a defenderthe firing angles a flat curtain wall can't. Same fortress, different jobs.

Every release is built from the tagged source on GitHub's runners and ships with SHA-256 sums, an SBOM and a signed build-provenance record. Verify a download with gh attestation verify <file> -R 1800bobrossdotcom-byte/bastion. Installers are not yet Authenticode-signed, so Windows SmartScreen will warn on first run.

Get Access

Access is donation-based. Enter $0.00 for free — or any amount you wish. Submit and we email your key instantly.

Get Access

Access is donation-based — enter 0.00 to get your key for free, or any USD amount you wish to pledge. We email your signed key immediately.

Optional — send BTC or ETH donation
BTCbc1qtf6fqllw7dny832ksw67p4a99txgvrct7u9e7d
ETH0x70B666c4e3EE5B2C9Ab92925F097330813D1848a

Any amount keeps development moving. Paste your email above and submit — your key is emailed regardless.

What Bastion Adds to Defender

Keep Defender on. Bastion doesn't replace it or compete with it — it gives you an independent local view and the evidence behind every alert.

Microsoft Defender+ Bastion
Malware prevention and real-time blockingAn independent second view of processes, persistence, DNS and files
Its own protection settingsDefender Watchdog: alerts if protection, tamper protection or signatures degrade, or a new exclusion appears
Cloud-delivered intelligenceLocal-first evidence: nothing leaves the device by default
Windows event log entriesA hash-chained event history that shows if it was edited afterwards
—Persistence drift: Run keys, services, scheduled tasks, hosts file, Startup folder
—Camera and microphone access log, per app
—Canary files and registry decoys that alert on any touch
—Operator receipts: what was seen, its SHA-256, what was done, and the audit trail

What You See When Running

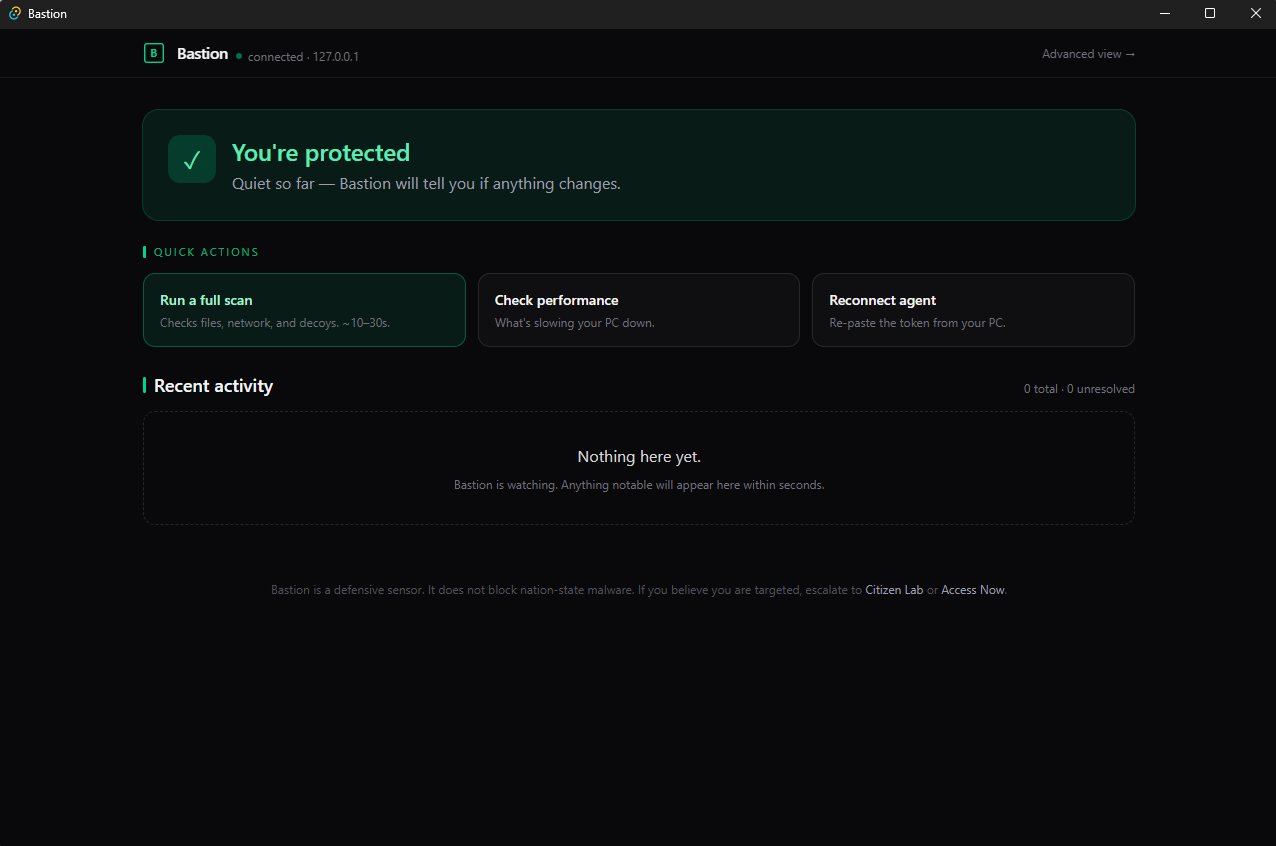
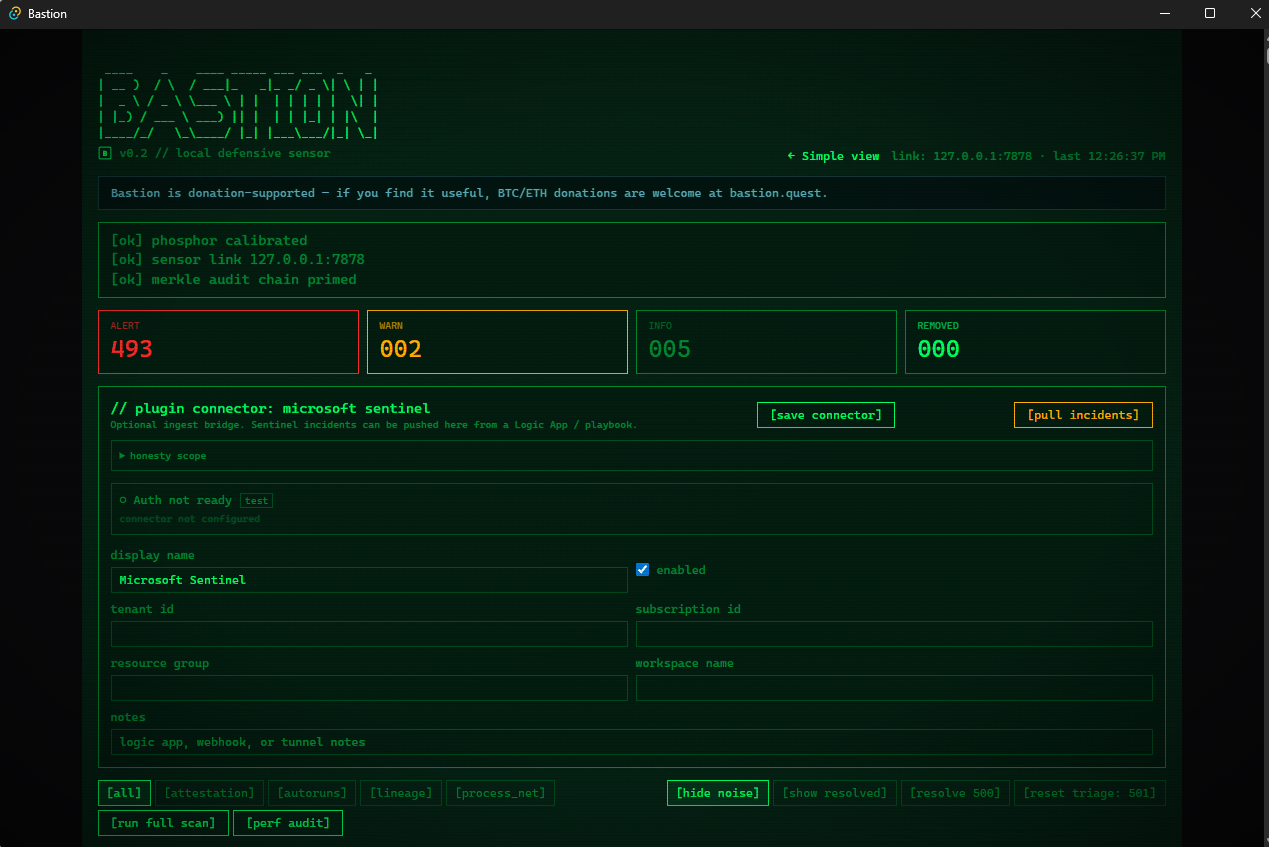
Actual screenshots of the desktop app. Two surfaces over the same agent: a calm consumer console for day-to-day, and a terminal-themed operator console for triage and response.

Bastion simple console — 'You're protected' status, Quick actions (Run a full scan, Check performance, Reconnect agent), Recent activity feed.
Simple view— at-a-glance status, one-click scan & perf audit, recent activity feed. File: src/app/app/page.tsx
Bastion operator/advanced console — ASCII BASTION banner, alert/warn/info/removed counters, Sentinel connector, event source filters, full triage controls.
Advanced view — full event chain, source filters, Sentinel connector, triage actions. File: src/app/app/operator/page.tsx

Detection & Response Checklist

Every line below is either shipped today, partially implemented, or on the roadmap. Nothing is marketed that the agent does not actually do.

Sensing (read-only)

  • [shipped]Recent process tree (proc_fp) with novel-fingerprint flagging
  • [shipped]Network indicator blocklist (URLhaus + OpenPhish, refreshed in background)
  • [shipped]File integrity monitor on Windows system paths + hosts file
  • [shipped]Canary / decoy tokens planted, watched for tamper
  • [shipped]Microsoft Defender event ingest (event log poll)
  • [shipped]Windows Firewall rule-change ingest
  • [shipped]Autoruns / persistence (Run keys, services, scheduled tasks)
  • [shipped]Camera / mic access enumeration (privacy registry log)
  • [shipped]DGA-style hostname heuristic on outbound DNS
  • [shipped]MalwareBazaar SHA256 hashlist scan-on-write

Recording & integrity

  • [shipped]Append-only event store (sqlite)
  • [shipped]Merkle audit chain over every event row (tamper-evident)
  • [shipped]Boot integrity rollup before steady-state detectors
  • [shipped]Attestation signing key sealed with Windows DPAPI — the API token is a plain file protected by your user profile
  • [shipped]Forensic export bundle (events, chain verification, head hash, quarantine manifests) — the zip itself is not signed yet

Response (operator action)

  • [shipped]Kill PID with audited reason
  • [shipped]Quarantine to evidence vault (file copied with sha256 + original path receipt before removal)
  • [shipped]Trust a fingerprint or a whole exe (suppresses future noise)
  • [shipped]Resolve / re-open per-event triage state
  • [shipped]Run full scan on demand
  • [shipped]Performance audit + elevated apply for safe recommendations
  • [partial]Junk cleanup, program review and machine health score — agent CLI + API in v0.4.0; console screen pending

Bridges

  • [shipped]Microsoft Sentinel incident pull (azure-cli auth)
  • [shipped]ntfy.sh push notifications (optional)
  • [shipped]Windows toast notifier on alerts
  • [partial]Webhook ingest for arbitrary upstream SIEMs — Sentinel-shaped only today

UI

  • [shipped]Severity counters (ALERT/WARN/INFO) clickable to filter
  • [shipped]Hide-noise toggle + risk classification chip on each row
  • [shipped]Per-event WHY explanation (causal chain + AI manager)
  • [shipped]Quarantine vault list — restore is on the roadmap
  • [shipped]Source filter chips (proc_fp / autoruns / camera_mic / …)

Roadmap (next updates)

  • [shipped]Unified scan engine (single chokepoint: dedupe + hash + MalwareBazaar match + auto-quarantine)
  • [shipped]Drop-directory watcher (Downloads / Desktop / Documents via ReadDirectoryChangesW)
  • [shipped]System-wide on-access scan via Microsoft-Windows-Kernel-File ETW (admin-gated, graceful fallback)
  • [partial]AMSI provider DLL (PowerShell / Office / .NET scan hook) — cdylib + COM exports — scaffold builds; IAntimalwareProvider2 vtable + named-pipe IPC pending; needs Trusted Signing to load on Win10 1903+
  • [partial]Kernel minifilter driver: pre-create capture + user-mode verdict bridge (fail-open on agent crash) — KMDF source + INF + user-mode bridge scaffold landed; needs WDK build + EV cert + altitude allocation from Microsoft
  • [roadmap]Signed & loaded driver in production (EV cert → optional Partner Center attestation signing → Anti-Virus altitude)
  • [shipped]ASR-style behavioural rules (Office→script-host, browser→LOLBin, encoded PowerShell, mshta remote URL, certutil downloader, WMI shell spawn, rundll32 side-load)
  • [roadmap]YARA into scan_engine (community + custom rules over every scanned file)
  • [shipped]Defender Watchdog (alert when real-time protection off / exclusions added / Tamper Protection disabled / signatures stale)
  • [roadmap]Driver / service drift surveillance (every new kernel driver: signer chain + Authenticode + first-seen) — BYOVD defence
  • [roadmap]Restore-from-vault button + sha256 verify on restore
  • [roadmap]YARA scan integration into quarantine pipeline
  • [roadmap]Generic webhook ingest schema (Splunk / Elastic / Wazuh)
  • [roadmap]Sigma rule loader for custom detections
  • [roadmap]Optional remote forwarder for multi-host triage
  • [roadmap]Tor / Tailscale-friendly secondary bind
  • [roadmap]macOS launchd + EndpointSecurity port of the agent
  • [roadmap]Linux auditd + inotify port of the agent
  • [shipped]Releases built from source in GitHub Actions with SHA-256 sums, SBOM and Sigstore build provenance — from v0.4.0
  • [shipped]Dependency audit (RustSec) on every change
  • [roadmap]Authenticode-signed installer — needs a code-signing certificate
  • [roadmap]Reproducible (bit-for-bit) builds
  • [roadmap]Signed forensic export zip
  • [roadmap]Independent security review

Honesty Notes

Support Development

Bastion is free. If it helps you, BTC or ETH donations keep development moving — any amount is welcome.

BTC: bc1qtf6fqllw7dny832ksw67p4a99txgvrct7u9e7d
ETH: 0x70B666c4e3EE5B2C9Ab92925F097330813D1848a

How Access Works

  1. 1. Enter your email and a USD donation amount ($0.00 = free).
  2. 2. Press Get Access Key — we email your signed key immediately.
  3. 3. Open /app, paste your key, then paste the agent bearer token from %APPDATA%\bastion\bastion\data\token.txt.
  4. 4. If you wish to donate, send BTC or ETH to the addresses above.